AI IN CYBERSECURITY

AI in Cybersecurity is a 4-week, 8-session professional course for SOC analysts, AppSec engineers, pentesters, and cloud security and vulnerability management engineers who want to use AI inside real security work.
What is this course
YOUR OWN SECURITY WORK, DONE WITH AI
You already know security.
Now learn where AI helps, where it fails, and how it gets attacked.
This is not a course about security fundamentals.
And it is not a machine learning course.
In week 1 you pick one real task from your job. By week 4 it is a working AI-assisted workflow, with numbers that show whether it helps, a threat model of your own agent and a plan to roll it out at work.
- 01
Know what AI can really do
Triage, summarization, enrichment and code review help today. A fully autonomous SOC or a tool that "finds every vulnerability" is still mostly a sales pitch. Learn to tell the two apart and to catch invented CVEs and confident wrong verdicts.
- 02
Attack and defend AI
Prompt injection, the OWASP Top 10 for LLM and Agentic Applications, excessive agency and MITRE ATLAS. Hijack a deliberately vulnerable agent, then fix it with least privilege and an approval step.
- 03
Build a workflow you can trust
Evaluation sets, precision and recall, guardrails, an audit trail and a rollout plan: an AI workflow your team can measure, explain and keep running.
Who is this for
BUILT FOR SECURITY PRACTITIONERS WHO WANT TO WORK AI-NATIVE
SOC Analysts
Who want AI to gather asset, user and threat intel context for alerts, analyze phishing and draft incident timelines, with the evidence behind every verdict.
AppSec Engineers
Who want to triage scanner findings at scale, review pull requests with AI agents and serve secure coding rules to AI coding tools.
Penetration Testers
Who want AI for recon, payload ideas and report writing, and need to know how to scope autonomous AI pentest platforms and check what they report.
Cloud Security Engineers
Who want a newly exploited CVE to trigger a read-only query of the asset inventory and a prioritized fix list.
Vulnerability Management Engineers
Who want to dedupe findings from several scanners, prioritize them with CISA KEV and EPSS, and route each one to the team that owns it.
Security Team Leads
Who need to measure what AI really changes, set the rules for which data goes to which model, and run a proof of value before buying AI security tools.
Curriculum
EIGHT SKILLS.
ONE MONTH.
- 01
LLMs and Agents for Security Work
What works today and what is still marketing, hallucination in security work, prompting for analysis, retrieval (RAG), tools, agents and MCP, and choosing a model.
- 02
The AI Attack Surface
Direct and indirect prompt injection, the OWASP Top 10 for LLM and Agentic Applications, the lethal trifecta, AI coding agents, the AI supply chain and MITRE ATLAS.
- 03
AI in AppSec and Vulnerability Management
Findings triage at scale, context that changes priority, owner attribution, verifying before ticketing, security review on pull requests and threat modeling from design docs.
- 04
AI in Security Operations and Offensive Testing
Alert triage and enrichment, phishing analysis, threat hunting in KQL, SPL or SQL, Sigma detection engineering, incident response support and AI in offensive testing.
- 05
Build Your Agent
One workflow from your job: scope, the simplest architecture that works, context, tools with read-only access by default, and public or synthetic data instead of your employer's.
- 06
Make It Trustworthy
An evaluation set of 30 to 50 labeled cases, spot checks, noise control, failure modes, red-teaming your own agent and an audit trail.
- 07
Run It in Production
Deployment, rollout, cost and latency, delivering AI findings to engineers, measuring impact, governance and buying AI security tools.
- 08
Capstone: Demo and Defense
Run your workflow on new cases, present the evaluation results and defend the threat model of your agent.
Instructor
LEARN FROM A PRACTITIONER
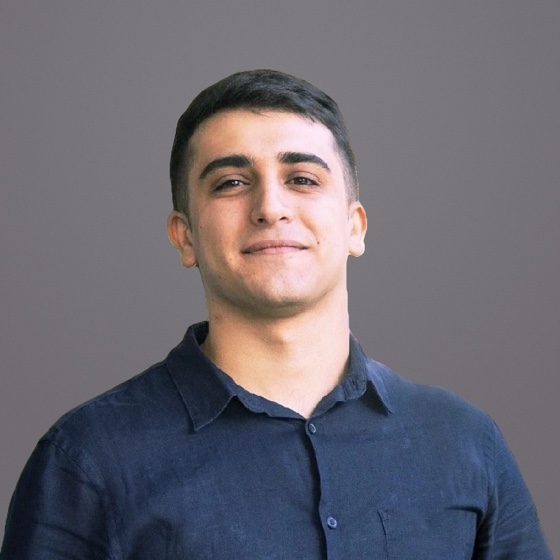
Suren Manukyan
Senior Application Security Engineer, ServiceTitan Armenia
Final Project
YOU DON'T GRADUATE WITH AN AI DEMO. YOU GRADUATE WITH A WORKING SECURITY WORKFLOW.
Each student builds one workflow from their own security work, runs it on new cases in the final session and defends it in front of the instructor and the group.
Join the Bootcamp- 01
A working AI workflow
Built on public datasets, synthetic data and sanitized samples, so nothing sensitive leaves your employer.
- 02
Numbers that show whether it helps
Precision and recall on your own evaluation set, compared against doing the task by hand.
- 03
A threat model and a rollout plan
Prompt injection tested through every input your agent reads, the controls you added, and a plan to roll it out at work.
Start your journey at ACA X
Master AI skills.
Build your future.
Lead the change.
Course Fee: 100,000 AMD
Get up to 100,000 AMD back if you submit your annual tax declaration and have income tax.
Secure your spot now
About ACA
ACA X IS BACKED
BY 10 YEARS OF
TECH EDUCATION
ACA X is the professional AI direction of Armenian Code Academy - one of Armenia's most established tech education institutions, founded in 2015.
For a decade, ACA has trained engineers, designers, product managers, and data professionals who now work at global companies, local unicorns, and fast-growing startups. ACA X is the next evolution -professional AI skills for everyone, not just engineers.
- 10+YEARS IN TECH EDUCATION
- 17K+TOTAL GRADUATES
- 100+PARTNER COMPANIES
- 300+TUTORS